Owner authority
Keep billing, account-level settings, administrative controls, and final ownership in the correct account.
 GHOST SPACEBrowser · Mobile · Automation
Separate authority from visibility. Roles control what a person may do; assignments control which profiles, phones, and tools they can see.
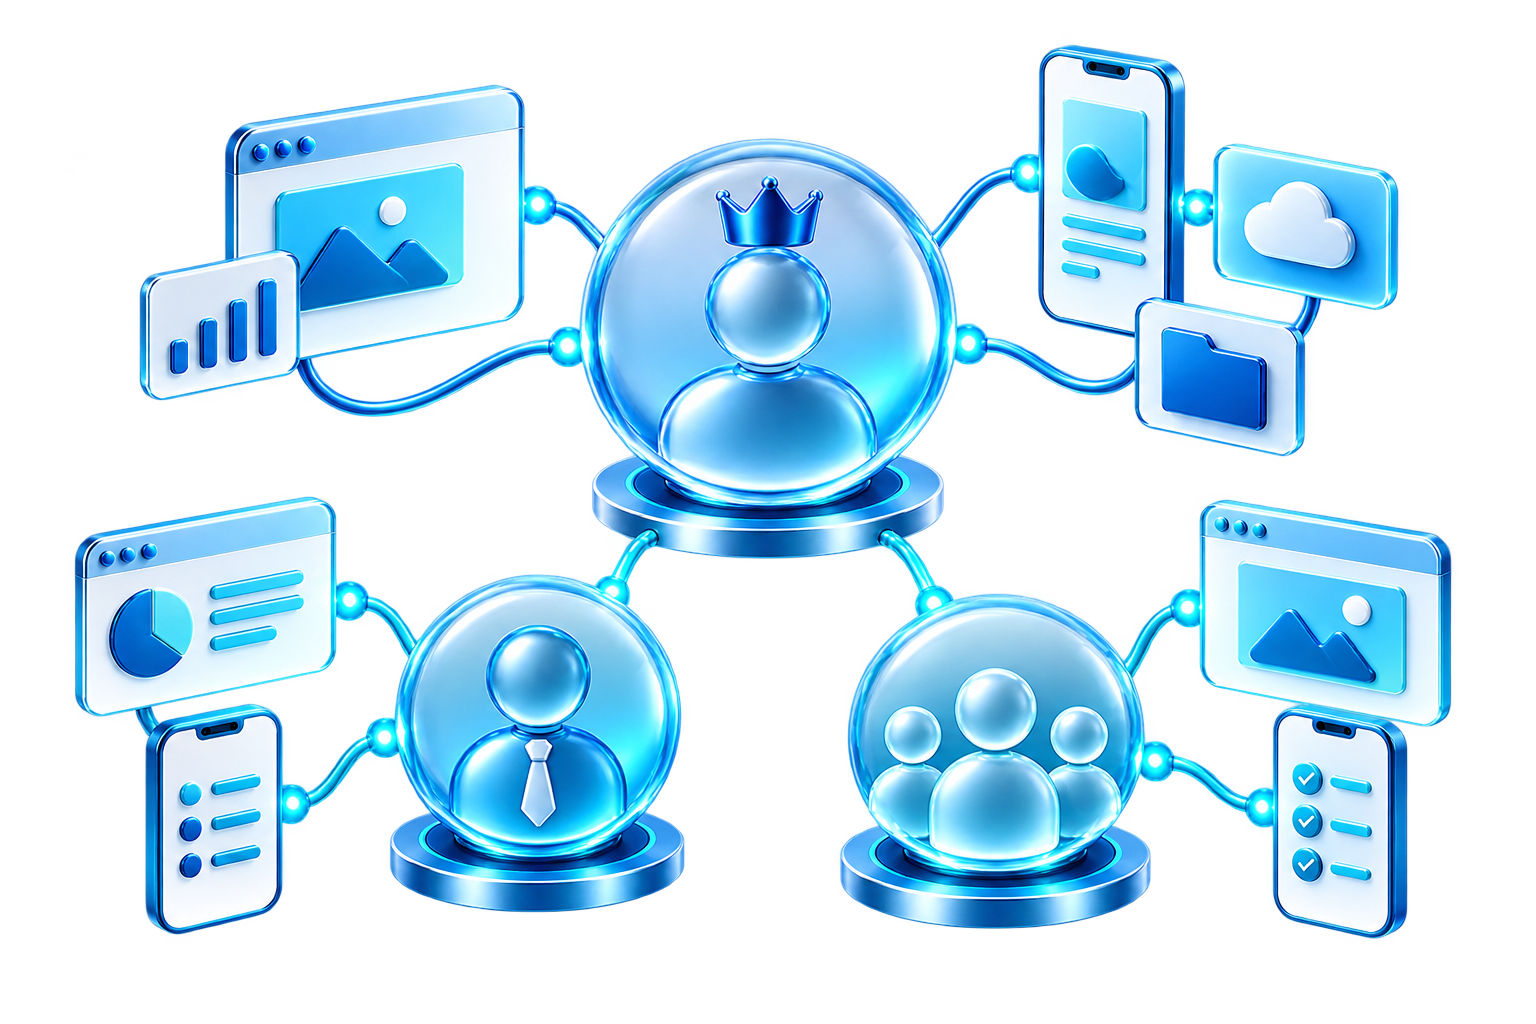 Access that follows your team
Roles establish authority while resource assignments keep each person focused on the profiles and tools connected to their work.
Keep billing, account-level settings, administrative controls, and final ownership in the correct account.
Delegate supported administration while keeping account ownership clearly defined.
Limit team members to the profiles, phones, folders, and tools explicitly connected to their work.
Control who may create, edit, delete, automate, or modify proxy settings by role and resource scope.
Give the next operator an established environment instead of asking them to rebuild context or share credentials.
Keep tickets, feedback, and account identity tied to the submitting user for cleaner follow-through.
A clear sequence keeps ownership, targets, and outcomes visible.